One key for every app and server.
One sign-in for your internal apps and your servers. Add someone once, and remove them once.
Fob is the identity provider for your team. New starters get their apps and servers on day one, contractors get only what you give them, and when someone leaves, you switch off one account.
Single sign‑on
Connect anything that speaks OIDC or SAML, from AWS and Grafana to the tools you built yourself. Assign each app to the groups that use it, and your team signs in once and finds them all on one page.
- OIDC
- SAML 2.0
- SCIM 2.0
- WebAuthn
- TOTP
- OpenSSH
Sign in with passkeys
Passkeys can't be phished or reused. Require one for the apps that matter, and check any password still in use against known breaches. If your accounts live in Google Workspace, Entra ID or Okta, people can sign in through that instead.
SSH without long‑lived keys
Sign in from your terminal and get an SSH certificate that expires on its own. There are no keys to hand out, and none to hunt down when someone leaves. Servers connect out to Fob, so they need no open inbound port, and terminal sessions are recorded for replay.
Sign‑on policies
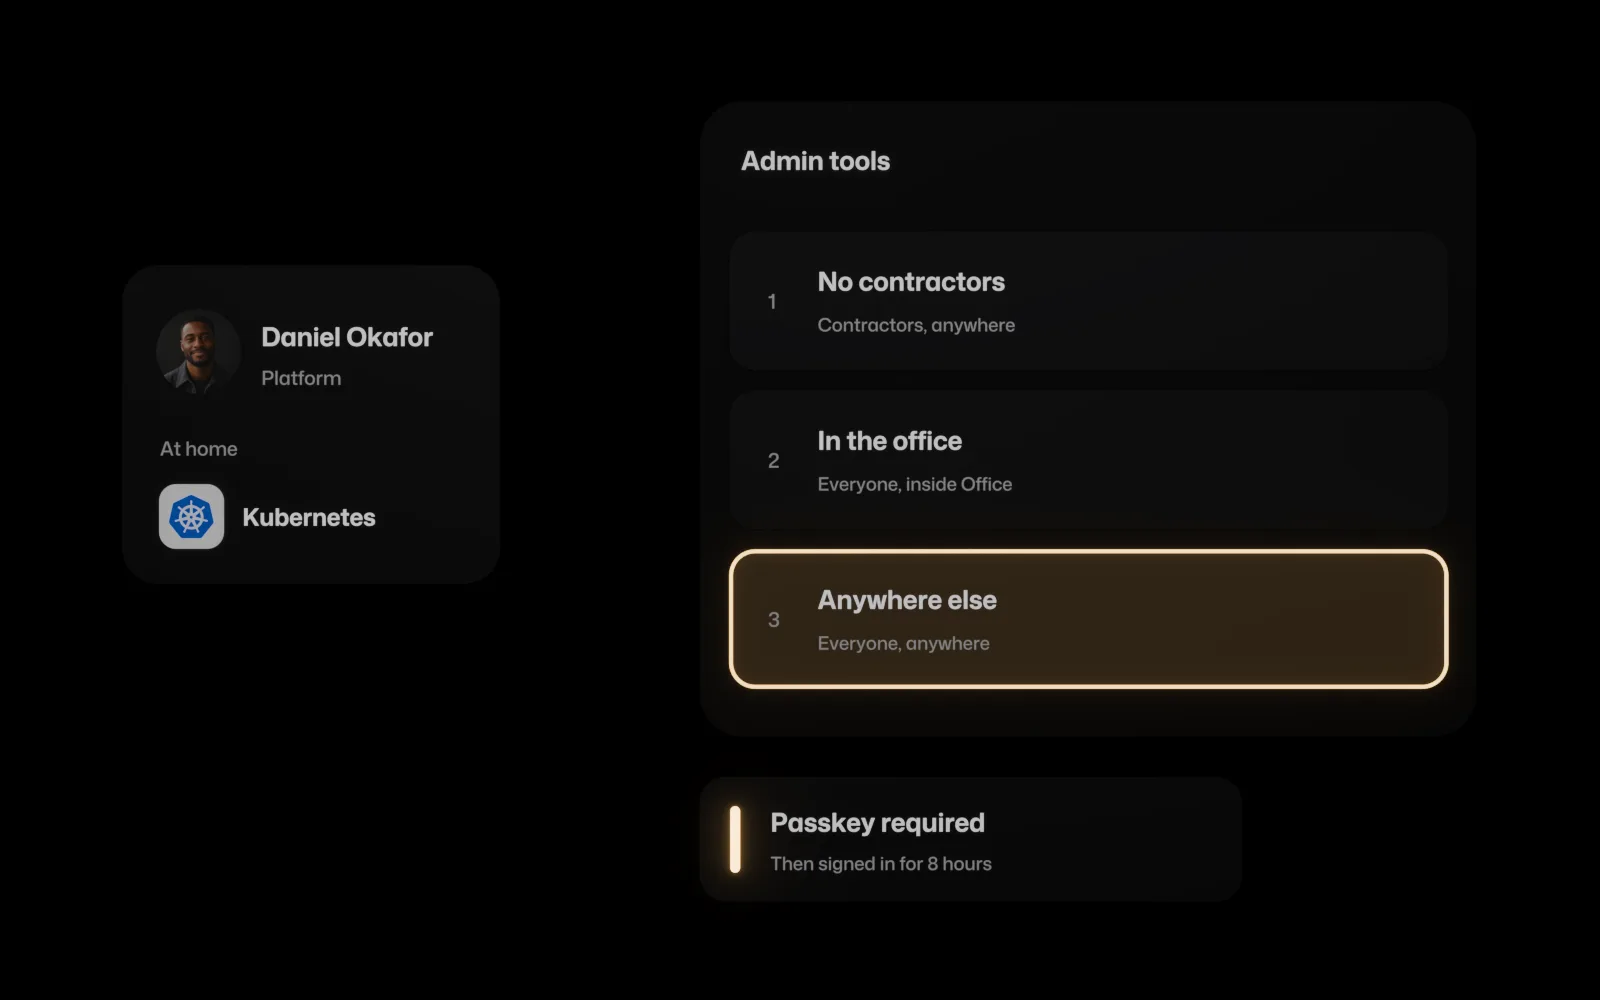
Decide what each app requires: a passkey, a second factor, a trusted network or a recent sign-in. Rules run in order and the first match decides, and you can check what any person would get before you rely on it.
Your keys, kept safe
Fob holds the keys to everything else you run, so it's built to give an attacker as little as possible to steal and you a record of everything that happened.
- A stolen password isn't enough
- Passkeys are on by default, and passwords are checked against known breaches.
- Nothing stays open for long
- Certificates expire on their own, and a leaver is cut off straight away.
- Encrypted at rest
- Signing keys, SSH CA keys and authenticator secrets.
- Your organization stands alone
- Its own directory, signing keys and sign-in host.
- You can see what happened
- Every sign-in and change is logged, and terminal sessions can be replayed.
- Open standards
- OIDC, SAML, SCIM and OpenSSH. Nothing needs a Fob SDK.
Give everyone their own key.
Single sign-on, passkeys and logs are on the free plan. Tell us about your team and we'll get you started.